ZeroDayEvil/ai-security-tool
A terminal, a pentest suite, and 12 AI agents walk into one app
One cross-platform app tries to swallow your SSH client, CVE scanner, and red-team workflow in a single AI-flavored package.
Collecting fresh signals — velocity needs a few days of history.
collecting data…
star history
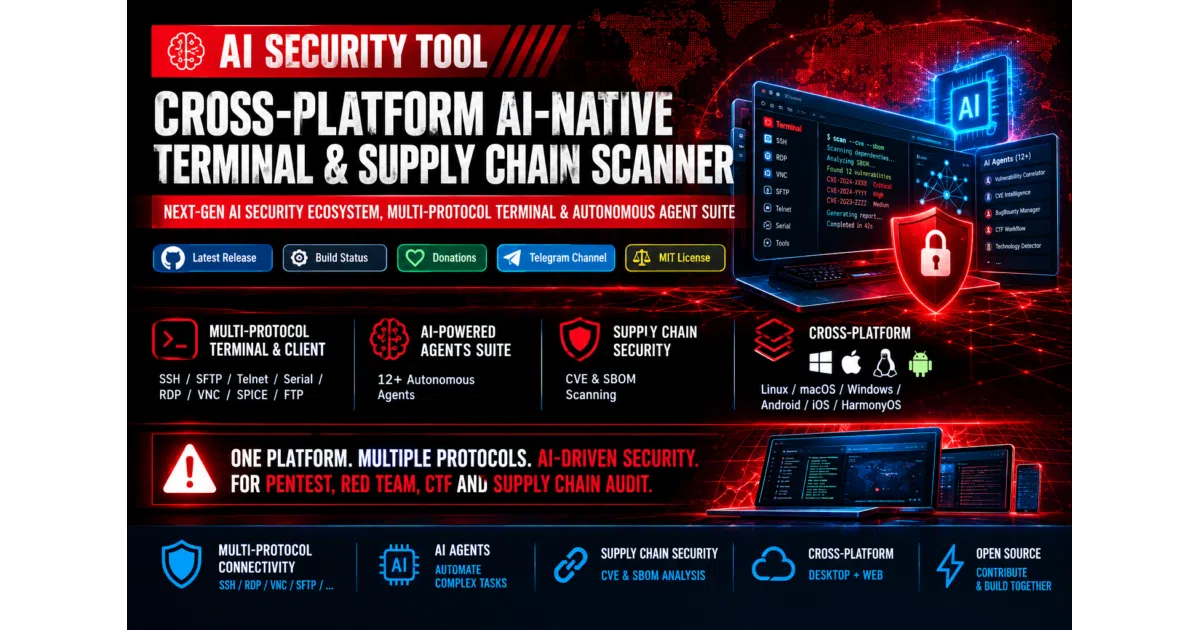
What it does AI Security Tool is a cross-platform terminal and security workbench that bundles multi-protocol remote access (SSH, SFTP, RDP, VNC, Telnet, Serial, SPICE, FTP) with supply-chain auditing (CVE and SBOM scanning) and a suite of 12+ autonomous AI agents. It ships as a desktop app for Linux, macOS, Windows, Android, iOS, and HarmonyOS, plus a web interface. The pitch: stop juggling a dozen utilities during audits, pentests, or CTFs.
The interesting bit
The agents are the differentiator — named things like IntelligentDecisionEngine (picks tools and tunes parameters), BugBountyWorkflowManager, and CTFWorkflowManager, backed by LLMs like DeepSeek and OpenAI for command suggestions, script generation, and terminal output analysis. It also leans into terminal-as-tool: Guake-style hotkey terminal, multi-session command broadcast, and double-click remote file editing over SFTP.
Key highlights
- Multi-protocol terminal with SSH tunneling, proxy support, and session broadcast to multiple hosts at once
- CVE and SBOM scanning for supply-chain audits, with LRU caching to speed repeat analysis
- Built-in API diagnostics for GraphQL, JWT, and REST endpoints
- Settings sync (bookmarks, themes, quick commands) via GitHub Gist or Gitee Snippets
- AI assistant supports DeepSeek, OpenAI, and custom APIs
Caveats
- The README’s “PoC repositories” are a wall of
CVE-2026-*identifiers — future-dated CVE numbers that don’t correspond to any real published vulnerability, which is a genuine trust question for a security tool - The repo’s primary language is HTML, so how much of the scanning and agent logic lives here versus in linked repos is unclear from the README alone
- “12+ agents” is asserted, not demonstrated — no benchmarks or worked examples in the source material
Verdict As a unified terminal-plus-AI workbench for CTF players and red-teamers who like everything in one window, it’s worth a look. But the future-dated CVE PoCs mean you should verify before trusting anything labeled as a vulnerability module.
Frequently asked
- What is ZeroDayEvil/ai-security-tool?
- One cross-platform app tries to swallow your SSH client, CVE scanner, and red-team workflow in a single AI-flavored package.
- Is ai-security-tool open source?
- Yes — ZeroDayEvil/ai-security-tool is open source, released under the MIT license.
- What language is ai-security-tool written in?
- ZeroDayEvil/ai-security-tool is primarily written in HTML.
- How popular is ai-security-tool?
- ZeroDayEvil/ai-security-tool has 563 stars on GitHub.
- Where can I find ai-security-tool?
- ZeroDayEvil/ai-security-tool is on GitHub at https://github.com/ZeroDayEvil/ai-security-tool.