N1nEmAn/sapper-v2
An AI legion that won a CTF on a quarter of the tokens
sapper-v2 orchestrates a commander, generals, and soldiers as a self-healing swarm — and beat teams burning 4.5x its token budget.
Collecting fresh signals — velocity needs a few days of history.
collecting data…
star history
What it does
sapper-v2 is a multi-agent orchestration harness for autonomous penetration testing in CTF-style competitions. One AI commander reads the board and dispatches; generals and soldiers attack targets in parallel inside tmux panes; a dumb pure-script watchdog keeps everything alive. Every finding settles into a layered fact-intent graph, so when an agent’s context saturates and it gets recycled, its successor inherits the playbook instead of starting from zero.
The interesting bit
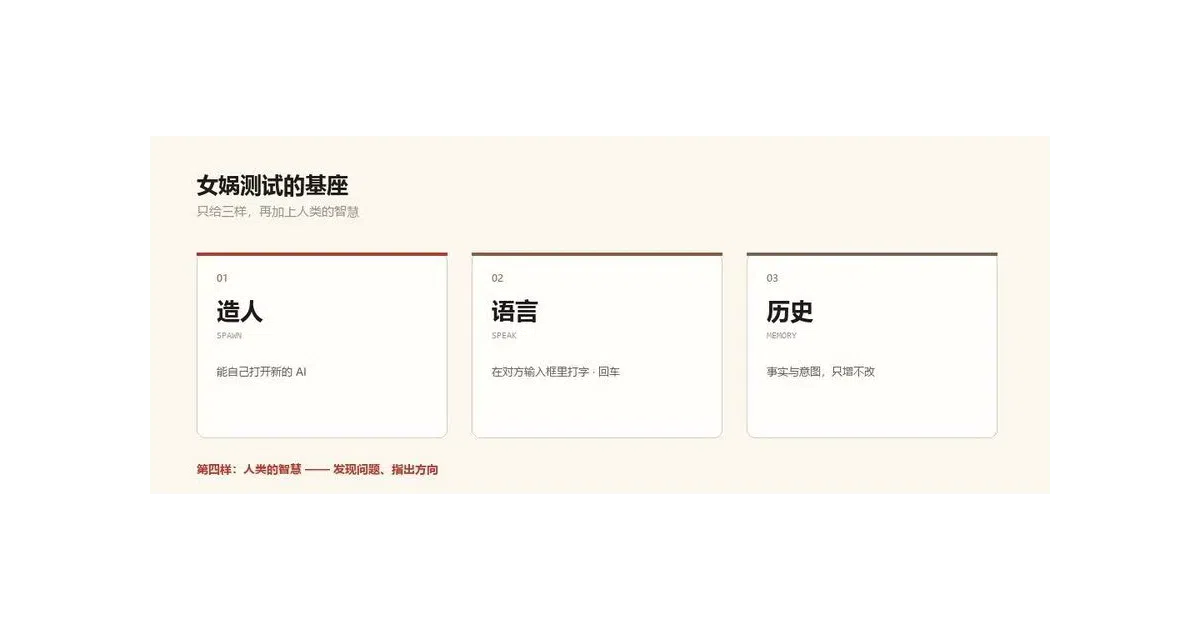
The whole thing is model-agnostic glue: swap the agent CLI, the model, even the 426-line doctrine file, and the mechanism survives. The authors frame it as a “Nüwa Test” — give AIs Create (spawn new sessions), Language (type into each other’s inputs), and History (the shared graph), and see if division of labor emerges. It did: the commander invented a signalman role, performance reviews, and ALL-CAPS workplace norms with zero pre-coded behavior.
Key highlights
- Won the 3rd Tencent Intelligent Attack-Defense online qualifier: 80.18/100, 85 flags, 8 hours fully unattended, 634 teams
- Same flag count as the runner-up, 25 seconds faster — on 1B tokens vs their 4.5B, via model tiering (heavy models decide, light models grind)
- Emergent tactics: reusable shellcode templates that swept a challenge family, an automatic pivot pipeline, isomorphism transfer across structurally identical challenges
- Late-game pace reportedly hit one solve per 3 minutes; soldier context saturation measured around ~260K tokens
- The general-purpose foundation (Create/Language/History) is split out as
nvwabase— pure Python stdlib, zero deps, agent-agnostic
Caveats
- Built for one specific competition format; the README itself steers other use cases toward
nvwabaseor a doctrine rewrite - The grander “Nüwa Test / AGI civilization” framing is philosophy layered on top of what is, at heart, a tmux orchestration harness — take it or leave it
- Authorized security testing only, per the project’s own disclaimer
Verdict
Worth a look if you build multi-agent systems or run CTF automation — the token economics and emergent-role stories are genuinely interesting. If you wanted a turnkey pentest tool, this is a competition harness with a philosophy attached, not that.
Frequently asked
- What is N1nEmAn/sapper-v2?
- sapper-v2 orchestrates a commander, generals, and soldiers as a self-healing swarm — and beat teams burning 4.5x its token budget.
- Is sapper-v2 open source?
- Yes — N1nEmAn/sapper-v2 is open source, released under the MIT license.
- What language is sapper-v2 written in?
- N1nEmAn/sapper-v2 is primarily written in Python.
- How popular is sapper-v2?
- N1nEmAn/sapper-v2 has 611 stars on GitHub.
- Where can I find sapper-v2?
- N1nEmAn/sapper-v2 is on GitHub at https://github.com/N1nEmAn/sapper-v2.