0sec-labs/0
A security research OS that runs in your browser, terminal, and agents
0sec's "0" wraps AI-driven vulnerability assessment, verification, and fixing into one workflow runner shared across browser, CLI, and MCP.
Collecting fresh signals — velocity needs a few days of history.
collecting data…
star history
What it does
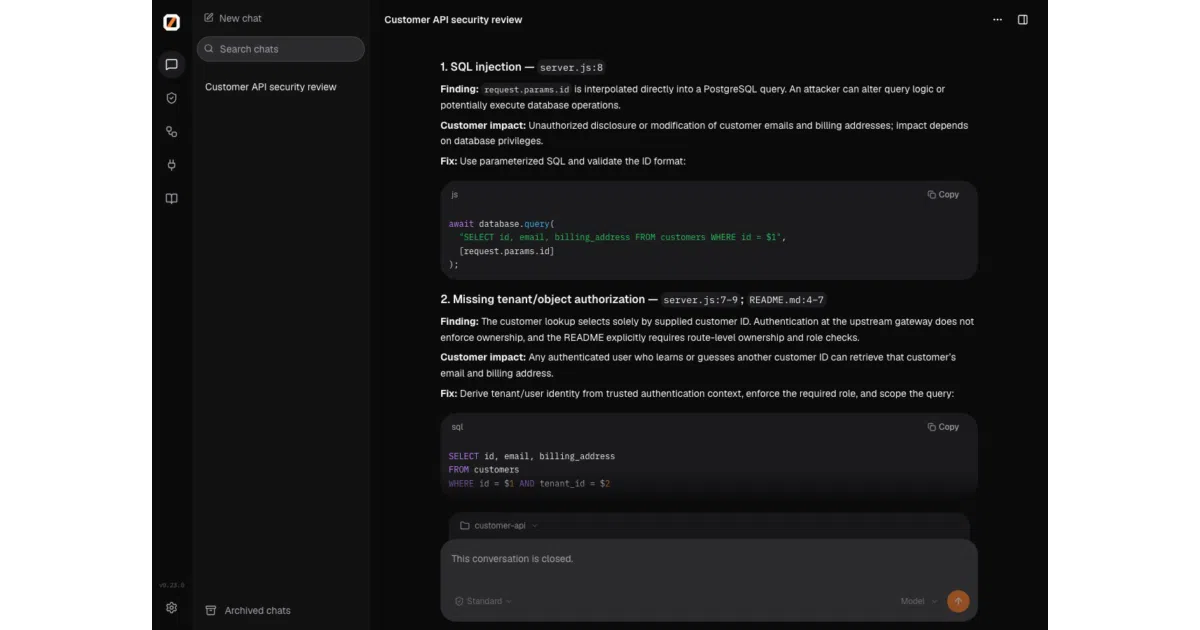
0 is an open-source, full-stack security toolkit: it assesses code (repos, dependencies, APIs, web configs, smart contracts, even native code), verifies findings with replay evidence, and proposes fixes with regression tests. The same workflow runner is exposed three ways — a browser “Command Center,” a terminal CLI, and an MCP server — so a coding agent can drive the same runs you started in the browser. It ships with 12 built-in templates covering things like scoped penetration tests and security research, all customizable.
The interesting bit
Findings are prioritized by business impact — affected customers, fraud, critical services — with a rationale attached, and anything it can’t assess stays explicitly “Not assessed” rather than guessed. CVSS is still there for technical severity. There’s also a “Learning” system that retains run activity and source-grounded notes locally, and saved workflows keep immutable revisions.
Key highlights
- One workflow engine shared across browser, CLI, and MCP; attached clients share the browser’s session and run lifecycle
- Verification produces replay evidence, not just a finding label
- Fix candidates come with regression tests
- Plugin integrations for GitHub, Semgrep, Snyk, Elastic, Jira, Linear, Slack, and more
- Dual-licensed MIT OR Apache-2.0; YC-backed
Caveats
- Explicitly a research preview — the README tells you to only assess authorized systems and review findings yourself
- The terminal defaults to “YOLO” mode (no confirmations); you have to opt into standard mode
- Requires configuring your own model provider before any AI workflow runs; macOS (Apple Silicon) and Linux only
Verdict
Worth a look if you run security reviews on codebases you own and want an agent-friendly pipeline instead of a pile of disconnected scanners. Skip it if you need production-grade, battle-tested tooling — it says “research preview” on the tin, and it means it.
Frequently asked
- What is 0sec-labs/0?
- 0sec's "0" wraps AI-driven vulnerability assessment, verification, and fixing into one workflow runner shared across browser, CLI, and MCP.
- Is 0 open source?
- Yes — 0sec-labs/0 is an open-source project tracked on heatdrop.
- What language is 0 written in?
- 0sec-labs/0 is primarily written in TypeScript.
- How popular is 0?
- 0sec-labs/0 has 501 stars on GitHub.
- Where can I find 0?
- 0sec-labs/0 is on GitHub at https://github.com/0sec-labs/0.