zgsfsec/Full-Chain-Sentinel-System
A pentest agent with a conscience (and an approval queue)
Full Chain Sentinel System wraps an LLM agent, Kali containers, and mobile device bridges into one bilingual console for authorized security testing.
Collecting fresh signals — velocity needs a few days of history.
collecting data…
star history
What it does
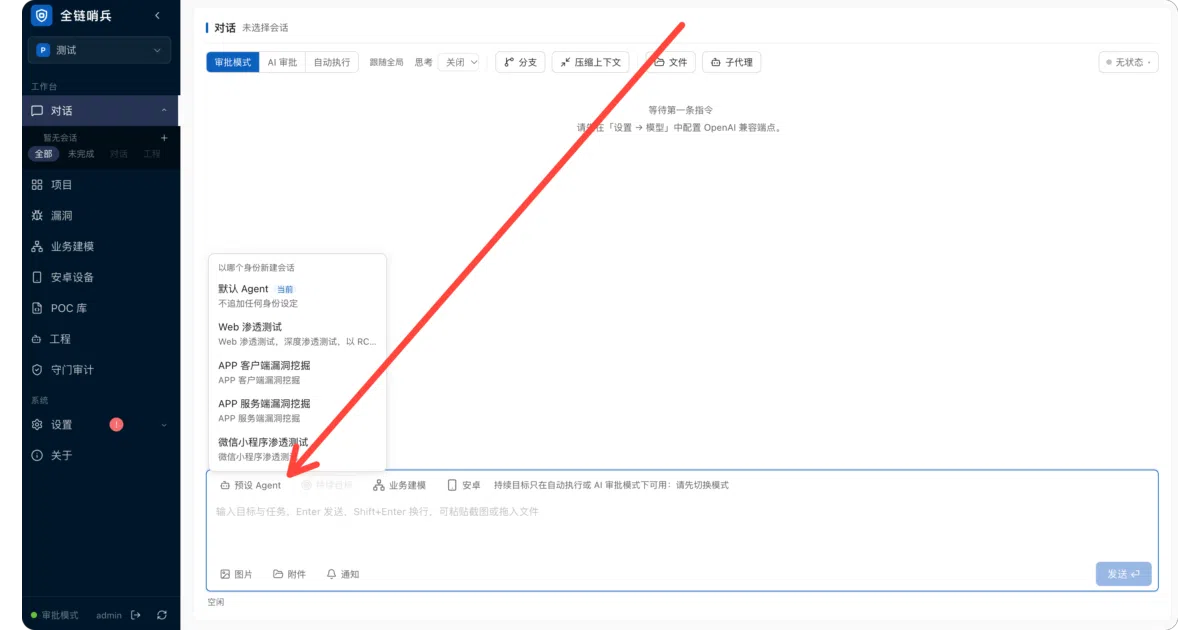
Full Chain Sentinel System (全链哨兵) is an authorized-pentest agent built as a fork of the MIT-licensed pi coding agent. It gives you a Chinese/English web console that manages Web, mini-program, and mobile testing: streaming chat, session forking, sub-agents, batch task orchestration, asset and vulnerability libraries, and Markdown reporting. Each project spins up a Kali work container behind a persistent gateway, so switching proxies doesn’t mean rebuilding your environment.
The interesting bit
The boring part is the value: it treats approval and audit as first-class features — human approval, auto-execution, or AI approval modes, with full call logs and session records. The agent can run arbitrary commands in auto mode, so the paper trail isn’t decoration. Mobile testing is handled via device bridges (DroidBridge for Android, SentinelBridge for iOS) supporting device reverse-connection, traffic capture, and dynamic analysis.
Key highlights
- Kali work containers with persistent gateways; SOCKS5/HTTP, WireGuard, OpenVPN, and hot-swappable exits
- Asset library, vulnerability hub with CVSS, evidence retention, and Markdown reports
- OpenAPI business modeling plus Nuclei POC subscription, search, and citation
- Intelligence integrations: FOFA, Quake, Hunter, Tavily, MCP, and local/remote plugin hosts
- Request replay, history search, screenshot evidence, and packaged file downloads
Caveats
- Explicitly for targets with written authorization only; the README repeats this and points to a security-boundary doc
- It’s a fork of
pi, not the upstream project — worth knowing if you track the upstream codebase - One bundled DOOM example extension is GPLv2, an odd license island in an otherwise MIT repo
Verdict
Worth a look if you deliver authorized pentest or app security work and want an agent that keeps receipts. Not for anyone hoping to point it at targets they don’t own — the project is blunt about that.
Frequently asked
- What is zgsfsec/Full-Chain-Sentinel-System?
- Full Chain Sentinel System wraps an LLM agent, Kali containers, and mobile device bridges into one bilingual console for authorized security testing.
- Is Full-Chain-Sentinel-System open source?
- Yes — zgsfsec/Full-Chain-Sentinel-System is open source, released under the MIT license.
- What language is Full-Chain-Sentinel-System written in?
- zgsfsec/Full-Chain-Sentinel-System is primarily written in TypeScript.
- How popular is Full-Chain-Sentinel-System?
- zgsfsec/Full-Chain-Sentinel-System has 723 stars on GitHub.
- Where can I find Full-Chain-Sentinel-System?
- zgsfsec/Full-Chain-Sentinel-System is on GitHub at https://github.com/zgsfsec/Full-Chain-Sentinel-System.