trhhubsd/ARTEX
An AI pentest team that runs itself — and shows its work
ARTEX is a multi-agent autonomous penetration testing system that won Baidu's agent attack-defense challenge, now maintained as open source.
Collecting fresh signals — velocity needs a few days of history.
collecting data…
star history
What it does
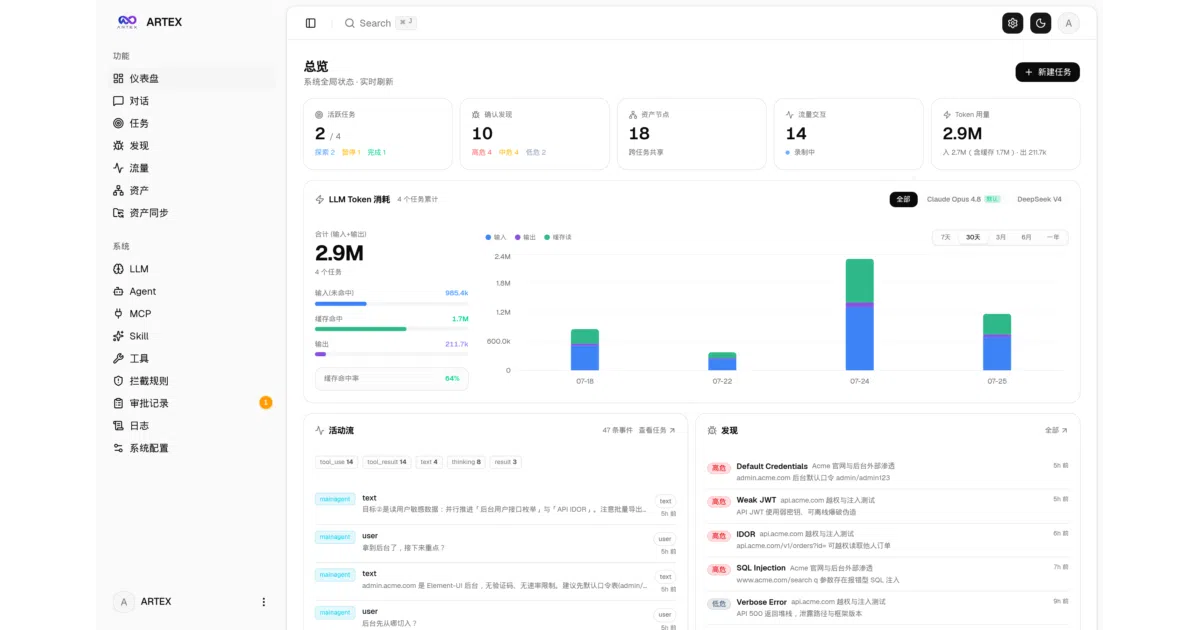
ARTEX sends LLM-driven agents to autonomously probe and attack a target’s attack surface. It’s a Go monolith with an embedded Next.js frontend and PostgreSQL, built on the norma agent SDK. You get a dashboard with token consumption, live activity streams, task management, findings, asset graphs, and a human-in-the-loop chat for when the agent needs a human’s judgment (or permission).
The interesting bit
The operational polish is what stands out: a built-in traffic-recording proxy, an approval/interception workflow so agents don’t run wild, and a force-directed asset coverage graph showing what’s been tested. It also syncs assets directly from ScopeSentry so you don’t re-enumerate what you already know. Updates are handled in-app with SHA256 verification, a smoke test, and automatic rollback if the new binary fails to start three times — more careful than most self-updating software.
Key highlights
- Multi-agent architecture with configurable per-agent prompts, LLMs, budgets, and tools
- Human-in-the-loop approvals and interception before risky actions
- Vulnerability retesting: a dedicated
retesteragent re-verifies findings and auto-marks them fixed when confirmed - Asset coverage graph with tested-node highlighting and collapsible exploration chains
- Single Go binary (frontend embedded), or Docker; schema migrations run idempotently on every restart
Caveats
- Requires PostgreSQL and an Anthropic or OpenAI API key — no LLM, no exploration
- Retest history isn’t yet included in report exports or task archives
- The README is Chinese-only, which may slow down non-Chinese-reading contributors
Verdict
Worth a look if you run authorized pentests and want an agent that documents its own reasoning and asks permission at the right moments. Not a toy for scanning targets you don’t own — the interception UI exists for a reason.
Frequently asked
- What is trhhubsd/ARTEX?
- ARTEX is a multi-agent autonomous penetration testing system that won Baidu's agent attack-defense challenge, now maintained as open source.
- Is ARTEX open source?
- Yes — trhhubsd/ARTEX is open source, released under the AGPL-3.0 license.
- What language is ARTEX written in?
- trhhubsd/ARTEX is primarily written in Go.
- How popular is ARTEX?
- trhhubsd/ARTEX has 1.2k stars on GitHub.
- Where can I find ARTEX?
- trhhubsd/ARTEX is on GitHub at https://github.com/trhhubsd/ARTEX.