BaaRai/ARTEX
An AI pentester that logs in like a human first
ARTEX is an English-language fork of a Chinese autonomous penetration-testing system — LLM agents crawling your asset graph, with humans kept in the loop.
Collecting fresh signals — velocity needs a few days of history.
collecting data…
star history
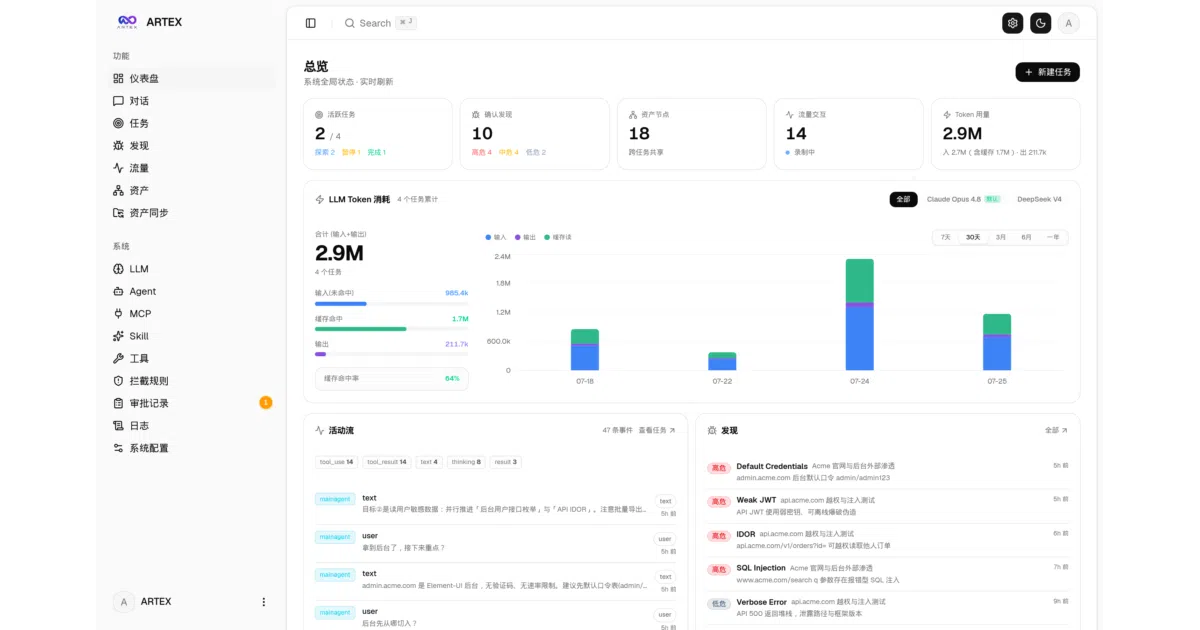
What it does ARTEX runs LLM-driven agents that autonomously explore and test a target’s attack surface, recording sessions, tool calls, traffic, and findings along the way. It’s a Go backend with an embedded Next.js frontend, backed by PostgreSQL, and it ships as a single binary or Docker stack. Everything the agents do — traffic, findings, assets — is searchable and linkable in the UI, and there’s a human-in-the-loop chat plus interception approvals so the operator can step in before anything risky happens.
The interesting bit The bundled browser extension is the clever part: you log into an authenticated target yourself (captchas, email OTP, 2FA and all), and your browsing becomes agent-visible evidence — the captured requests land in the traffic store like proxy recordings, ready to bind to findings. It also syncs assets from ScopeSentry so you don’t re-collect what you already scanned.
Key highlights
- LLM-agnostic: Anthropic, OpenAI, or a keyless local Ollama server, configurable in the UI
- Force-directed asset coverage graph showing what’s been tested, with node collapse/expand
- Interception approvals and global approval records with expandable detail views
- “Restart equals migrate”: the binary idempotently re-runs
schema.sqlon every start, no manual migrations - Ships with common pentest tools (nmap, curl, ripgrep, etc.) baked into the Docker image
Caveats
- This is a fork with translated docs — the original is by Autumn-27, and the repo history was rewritten in October 2026, so older clones need a manual reset
- No published Docker image; you build from checkout, and the previous default image pointed at a namespace that no longer hosts it
- Requires PostgreSQL and an LLM key (or local Ollama) — it won’t do much without both
Verdict Worth a look if you run authorized pentests and want an agent that works your asset graph while you supervise. If you wanted a fully hands-off scanner, the interception-approval workflow will feel like friction — by design.
Frequently asked
- What is BaaRai/ARTEX?
- ARTEX is an English-language fork of a Chinese autonomous penetration-testing system — LLM agents crawling your asset graph, with humans kept in the loop.
- Is ARTEX open source?
- Yes — BaaRai/ARTEX is open source, released under the AGPL-3.0 license.
- What language is ARTEX written in?
- BaaRai/ARTEX is primarily written in Go.
- How popular is ARTEX?
- BaaRai/ARTEX has 1.2k stars on GitHub.
- Where can I find ARTEX?
- BaaRai/ARTEX is on GitHub at https://github.com/BaaRai/ARTEX.