Autumn-27/ARTEX
AI pentesting that actually keeps receipts
ARTEX is an autonomous penetration-testing system that won Baidu's 'agent+' challenge by making every AI-driven attack auditable and interceptable.
Collecting fresh signals — velocity needs a few days of history.
collecting data…
star history
What it does
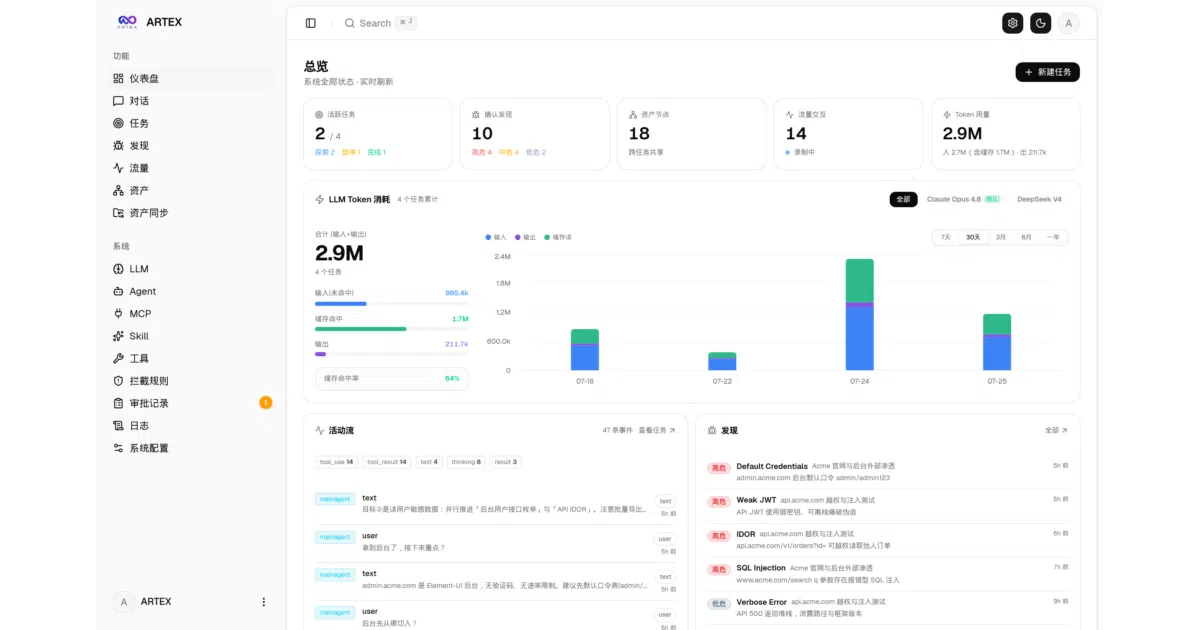
ARTEX is an autonomous penetration-testing platform that wraps a Go backend and Next.js frontend around LLM-driven reconnaissance and exploitation. It gives red-team operators a web dashboard to launch tasks, map assets in force-directed graphs, and review findings, while keeping the agent on a short leash. The system stores state in PostgreSQL and ships as either a single compiled binary or a Docker stack.
The interesting bit
Most agent tools treat oversight as an afterthought; ARTEX treats it as the architecture. Every tool request is fingerprinted with SHA-256, fed to a context-review model under strict byte limits, and gated by human or automated approval before execution. The docs even admit when concurrent identical calls cannot be disambiguated—displaying “unassociated” rather than fabricating audit trails.
Key highlights
- Won Baidu’s “agent+” attack-defense challenge; built in Go with an embedded Next.js UI
- Human-in-the-loop intercepts with persistent tool-call IDs, rollback-capable self-updates, and automatic database migrations on restart
- Syncs external attack surface data directly from ScopeSentry to avoid redundant reconnaissance
- Supports remote MCP servers via HTTP or legacy SSE for extending agent capabilities
- Audit logs distinguish between what was sent to the review model versus raw session transcripts, preserving old schema versions rather than rewriting history
Caveats
- In-app updates swap only the binary, leaving Docker image toolchains like
nmapandplaywrightstale unless you manually pull the new image - Running the raw
./artexbinary instead of the providedstart.shbreaks the self-update restart mechanism - The Norma SDK approval hooks lack call IDs, so concurrent identical tool requests may show as unassociated in the audit trail
Verdict
Red-team operators and security engineers who want LLM-driven scanning without blind trust should look here. If you are not building an offensive security pipeline, this is narrowly specialized tooling.
Frequently asked
- What is Autumn-27/ARTEX?
- ARTEX is an autonomous penetration-testing system that won Baidu's 'agent+' challenge by making every AI-driven attack auditable and interceptable.
- Is ARTEX open source?
- Yes — Autumn-27/ARTEX is an open-source project tracked on heatdrop.
- What language is ARTEX written in?
- Autumn-27/ARTEX is primarily written in Go.
- How popular is ARTEX?
- Autumn-27/ARTEX has 1k stars on GitHub.
- Where can I find ARTEX?
- Autumn-27/ARTEX is on GitHub at https://github.com/Autumn-27/ARTEX.